Prior to the emergence of the Model Context Protocol (MCP), software engineering teams attempting to connect foundation models to internal databases, version control systems, and business platforms were compelled to build proprietary bespoke connectors. This uncoordinated explosion of custom adapters created an intractable N×M integration matrix. MCP functions as the definitive USB-C standard for enterprise AI context.
1. Resolving the Tool Fragmentation Dilemma with MCP
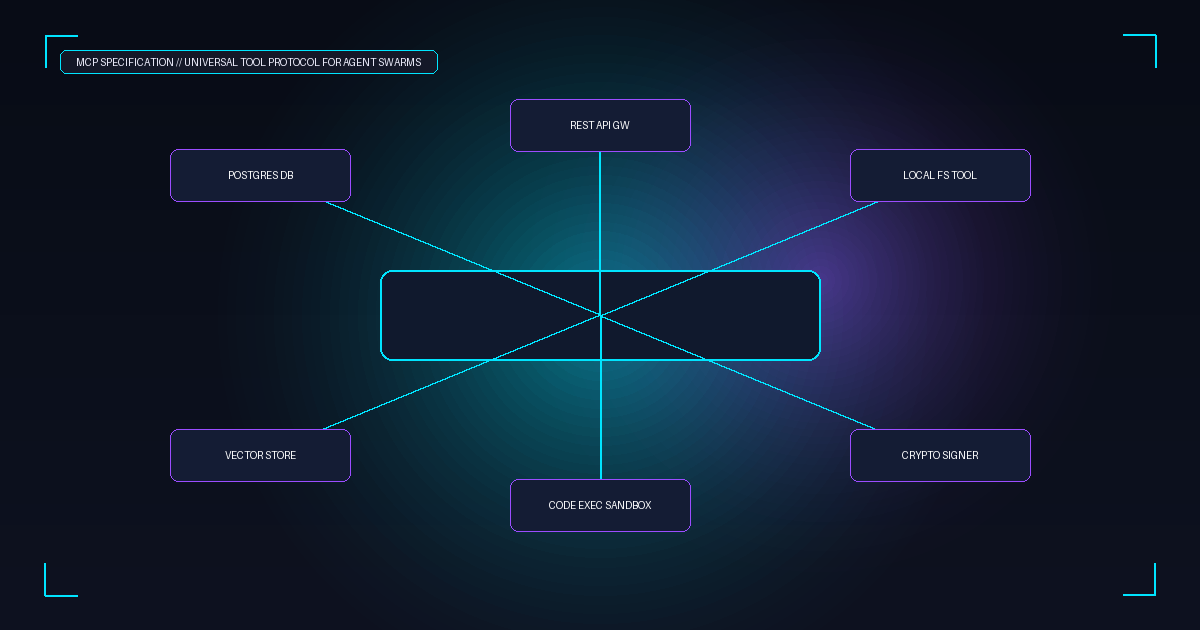
When heterogeneous models (Claude, GPT, DeepSeek, sovereign on-premise engines) interact with hundreds of operational systems (Postgres, Git, Salesforce, Kafka), maintaining brittle point-to-point glue code drains engineering bandwidth.
MCP decouples AI Hosts (runtime environments executing the models) from MCP Servers (lightweight microservices surfacing typed data resources, executable tools, and system prompts). All protocol exchanges adhere to JSON-RPC 2.0, supporting either standard input/output (stdio) pipelines or secure remote transports via Server-Sent Events (SSE).
Least-Privilege Security Sandbox: Unlike unrestricted API integrations, MCP Servers operate within isolated containers under least-privilege security boundaries. The model receives validated JSON Schema representations and never gains direct credentials or shell execution access to host systems.
2. Decentralized Agent Swarm Coordination
With standardized tool exposure, Multi-Agent Swarm Architectures reach production resilience. Rather than relying on a brittle monolithic agent overloaded with conflicting system prompts, the architecture partitions cognitive tasks across specialized autonomous agents:
- Architect / Planner Agent: Deconstructs organizational objectives into asynchronous Directed Acyclic Graphs (DAGs).
- Specialized Worker Agents: Consume dedicated MCP Servers (e.g., executing cryptographic ledger queries or generating compliance reports).
- Governance Auditor Agent: Validates outputs against strict data loss prevention (DLP) and enterprise compliance rules prior to state persistence.
3. Production Implementation at Better2Better
At Better2Better, we embed MCP as the default communications bus across all bespoke enterprise systems. Our custom platforms ensure that any operational backend—from instant payment gateways to ERP databases—surfaces as an audited MCP Server within minutes, empowering internal agents without requiring core architecture refactoring.
4. MCP Protocol Lifecycle Overview
| Phase | JSON-RPC Method | System Behavior |
|---|---|---|
| 1. Handshake | initialize |
Protocol version negotiation and bidirectional capability exchange. |
| 2. Discovery | tools/list |
Server broadcasts JSON schemas containing tool signatures and descriptions. |
| 3. Tool Execution | tools/call |
Host triggers tool execution with validated parameters inside secure runtime. |
| 4. Dynamic Resources | resources/subscribe |
Agents receive real-time push events whenever monitored enterprise records change. |
5. Technical References & Protocol Specifications
Open Specifications & Systems Research:
- Anthropic Protocol Working Group (2024). Model Context Protocol Specification v1.0. Model Context Protocol Open Standard.
- JSON-RPC Working Group (2010). JSON-RPC 2.0 Specification. JSON-RPC Org.
- Wu, Q., Bansal, G., Zhang, J., et al. (2023). AutoGen: Enabling Next-Gen LLM Applications via Multi-Agent Conversation. arXiv:2308.08155.
Enterprise AI Security Guarantees & Cryptographic Code Audits
Deploying autonomous agent swarms without hardened defense layers is the single highest operational risk in modern computing. At Better2Better, our dedicated team led by Felipe Siqueira and Dr. Helena Vance performs deep architectural code audits, neutralizing prompt injections, securing vector memories in gVisor sandboxes, and orchestrating execution across encrypted hardware enclaves.
What can we build for you today?
Enjoyed this deep dive? Deploy enterprise autonomous AI agent swarms with guaranteed security hardening clicking here!
🤖 Deploy Autonomous AI Agents via WhatsAppEnterprise AI Security Guarantees & Cryptographic Code Audits
Deploying autonomous agent swarms without hardened defense layers is the single highest operational risk in modern computing. At Better2Better, our dedicated team led by Felipe Siqueira and Dr. Helena Vance performs deep architectural code audits, neutralizing prompt injections, securing vector memories in gVisor sandboxes, and orchestrating execution across encrypted hardware enclaves.
What can we build for you today?
Enjoyed this deep dive? Deploy enterprise autonomous AI agent swarms with guaranteed security hardening clicking here!
🤖 Deploy Autonomous AI Agents via WhatsApp